Disclosure: Some links on this page are affiliate links. We may earn a commission if you make a purchase through them, at no additional cost to you.
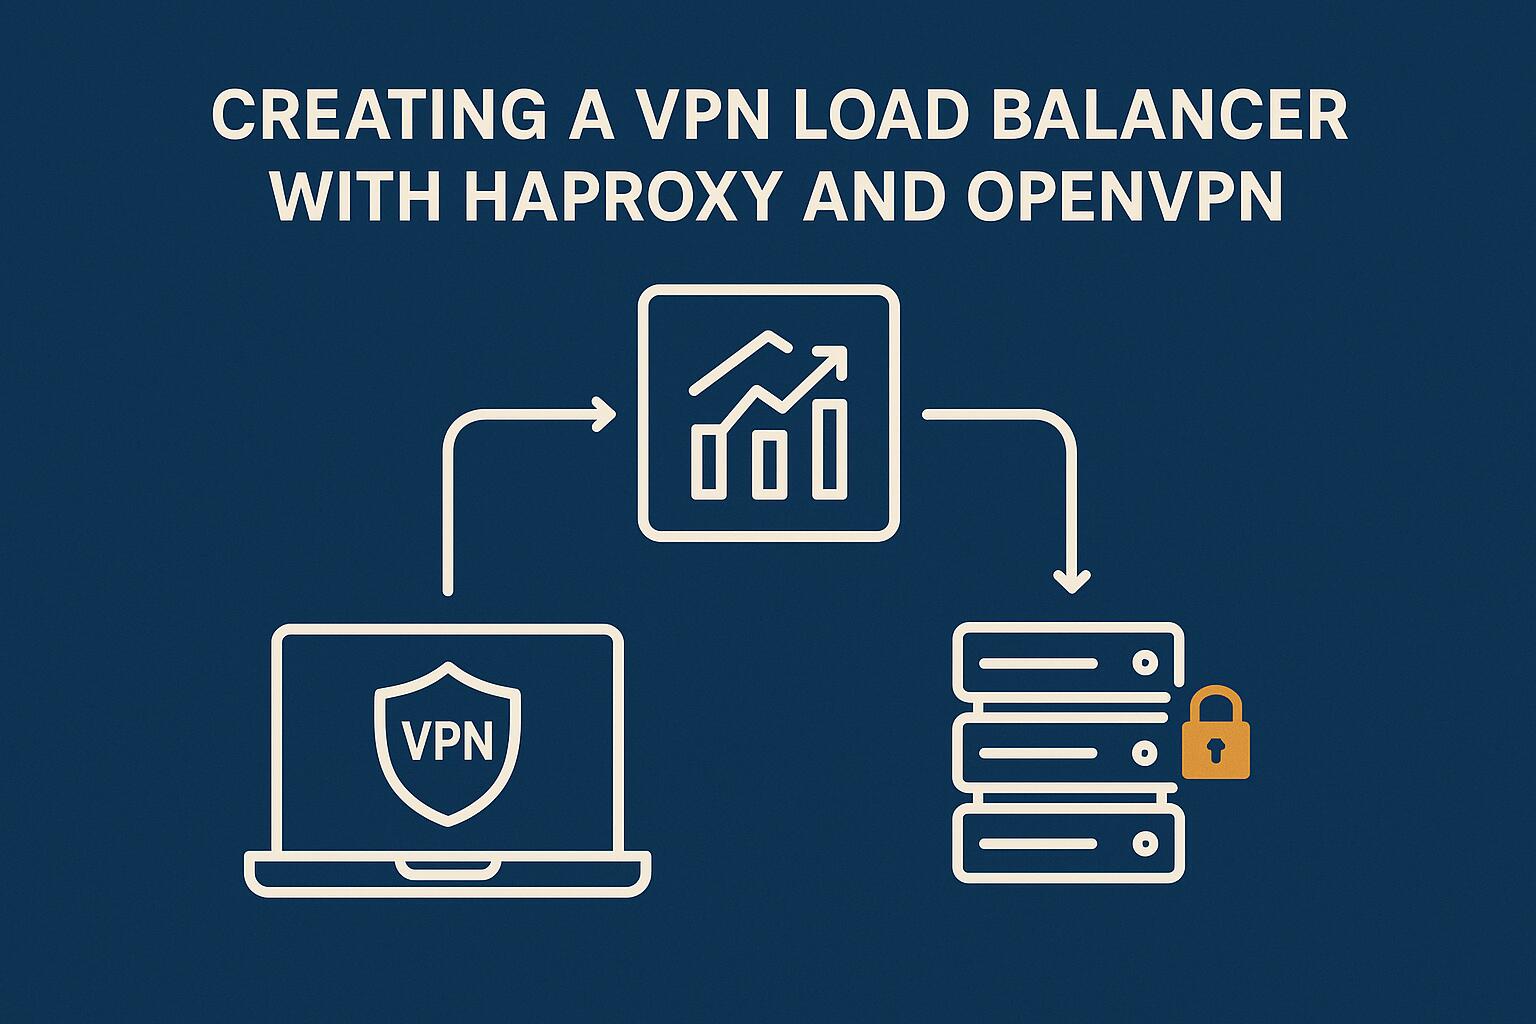
When scaling a VPN infrastructure, ensuring high availability and fault tolerance is crucial. Using a load balancer such as HAProxy in conjunction with OpenVPN can optimize performance, reduce downtime, and distribute traffic evenly across multiple VPN servers. This article covers the steps to create a robust VPN load balancer using HAProxy and OpenVPN.
Prerequisites
Before you begin, make sure you have the following:
- Two or more OpenVPN servers set up and running.
- A server where HAProxy is installed and configured.
- Root or sudo access on all servers involved.
- A basic understanding of HAProxy and OpenVPN configuration.
Step 1: Install HAProxy
HAProxy is a powerful load balancer that can distribute traffic across multiple OpenVPN servers. To get started, install HAProxy on the server that will act as the load balancer. On a Debian-based system, use the following commands:
sudo apt update
sudo apt install haproxy
Once installed, enable HAProxy to start on boot:
sudo systemctl enable haproxy
sudo systemctl start haproxy
Step 2: Configure HAProxy for OpenVPN
Next, you need to configure HAProxy to load balance between your OpenVPN servers. The configuration file for HAProxy is located at:
/etc/haproxy/haproxy.cfgOpen this file with your preferred text editor:
sudo nano /etc/haproxy/haproxy.cfgWithin the configuration file, set up a frontend and backend for the OpenVPN service. Below is an example configuration:
frontend openvpn_front
  bind *:1194
  mode tcp
  default_backend openvpn_back

backend openvpn_back
  mode tcp
  balance roundrobin
  server vpn1 10.0.0.1:1194 check
  server vpn2 10.0.0.2:1194 check
In this configuration, we are using a round-robin load balancing method to distribute connections between two OpenVPN servers (vpn1 and vpn2). The frontend section listens for traffic on port 1194 (the default OpenVPN port), while the backend directs the traffic to the available OpenVPN servers. Adjust the IP addresses and server details as needed.
Step 3: Enable HAProxy SSL/TLS Termination (Optional)
If you want to enable SSL/TLS termination on the HAProxy server, you need to configure it to decrypt incoming SSL traffic before forwarding it to the OpenVPN servers. This is useful if you want to offload the encryption from the OpenVPN servers.
First, obtain an SSL certificate for your domain. Once you have the certificate and private key, store them in a directory such as /etc/ssl/:
/etc/ssl/certs/openvpn-cert.pem
/etc/ssl/private/openvpn-key.pem
Then, modify the HAProxy frontend configuration to enable SSL termination:
frontend openvpn_front
  bind *:443 ssl crt /etc/ssl/certs/openvpn-cert.pem
  mode tcp
  default_backend openvpn_back
With this setup, HAProxy will handle the SSL handshake and decrypt the traffic before passing it to the OpenVPN server over a plain TCP connection.
Step 4: Configure OpenVPN Server for HAProxy
Each OpenVPN server must be configured to allow for proper handling of client connections routed through HAProxy. In the OpenVPN server configuration file (typically located at /etc/openvpn/server.conf), ensure the following settings:
port 1194
proto udp
dev tun
server 10.8.0.0 255.255.255.0
keepalive 10 120
persist-key
persist-tun
These settings allow OpenVPN to listen on port 1194 and ensure the server remains available to handle new connections. Additionally, ensure the server is configured to allow traffic from the HAProxy server’s IP.
Step 5: Test the Configuration
Once HAProxy and OpenVPN are configured, it’s time to test the load balancing setup. You can verify that HAProxy is forwarding traffic correctly by checking the OpenVPN server logs:
tail -f /var/log/openvpn.logAdditionally, you can use tools such as netcat (nc) or OpenVPN client to test the connection:
nc -vz 1194If everything is configured correctly, you should see HAProxy load balancing the connections across the OpenVPN servers.
Step 6: High Availability and Failover
To ensure high availability, configure HAProxy to handle failover scenarios. This can be achieved by setting the “check” directive for each OpenVPN server in the backend configuration. HAProxy will automatically stop sending traffic to a server that becomes unreachable, ensuring minimal disruption to users.
Here’s an updated example for the backend configuration with failover:
backend openvpn_back
  mode tcp
  balance roundrobin
  server vpn1 10.0.0.1:1194 check fall 3 rise 2
  server vpn2 10.0.0.2:1194 check fall 3 rise 2
In this configuration, the “fall” parameter specifies the number of failed checks before a server is considered down, and the “rise” parameter defines how many successful checks are required to bring a server back online.